Cyber Security · A solution area of Infoesearch

Find the weak spots, fix what is real, and prove you are secure.

Enterprise security testing, monitoring, response and compliance, run the Infoesearch way: AI does the heavy, repetitive work, and security engineers confirm every finding and own every recommendation. No alert floods, no unverified reports.

At a glance
Showcase product mAUDIT
Disciplines Test · Monitor · Respond · Comply
Every finding Checked by an engineer
Testing rule Authorised, in writing
Engagement Project · Retainer · Managed
The challenge

Attackers only need one gap. Most security teams cannot look everywhere at once.

More to defend every quarter

New web apps, APIs, cloud accounts and SaaS tools appear faster than any security team can review them, and each one is a new way in.

Scanners raise noise, not answers

Automated tools produce long lists of possible issues. Teams lose weeks separating real risks from false alarms, and the real ones wait.

Regulators and customers want proof

ISO 27001, SOC 2, PCI DSS, India's DPDP Act and CERT-In's six-hour incident reporting all ask for evidence, not intentions.

Skilled people are scarce

Experienced testers and analysts are hard to hire and harder to keep busy year-round. Most enterprises need them in bursts, at short notice.

Our solution

One security partner, from the first test to the audit report.

Infoesearch brings testing, monitoring, response and compliance under one roof, so the weaknesses found in a test feed straight into the fixes, the monitoring rules and the evidence your auditors ask for, instead of living in four vendors' reports.

It is the same Human in Command model we run across our media, localization and trust & safety work: AI covers the ground quickly and tirelessly, and experienced people decide what is real, what matters most and what to do about it.

Enterprise services

Every security discipline an enterprise needs, under one roof.

Take one service or the whole programme: as a one-off project, a yearly retainer, or a fully managed service. Every engagement is scoped with you, and nothing is tested without written authorisation.

Test
Offensive security

Find weaknesses the way an attacker would, before an attacker does.

Web application security testing mAUDIT
AI-assisted, engineer-verified testing of your websites and web apps, with proof and fixes.
API security testing
REST and GraphQL APIs tested for broken access control, injection and data exposure.
Mobile app testing
Android and iOS apps and the services behind them.
Network & infrastructure VAPT
External and internal vulnerability assessment and penetration testing.
Cloud security assessment
AWS, Azure and Google Cloud configuration, identity and exposure review.
Red team exercises
Goal-based attack simulation across people, process and technology.
Monitor & respond
Security operations

See threats early and act on them fast, around the clock.

Managed detection & response
Your logs and alerts watched by analysts, with AI triage and human escalation.
Vulnerability management
Continuous scanning, prioritised by real risk, tracked to closure.
Incident response
On-call responders to contain, investigate and recover, by retainer or on demand.
Threat & brand monitoring
Leaked credentials, impersonating domains and fake apps, drawing on our media-intelligence work.
Phishing simulation & awareness
Realistic campaigns and short training that changes behaviour.
Comply
Governance, risk & compliance

Meet the standard, and keep the evidence ready for the audit.

ISO 27001 & SOC 2 readiness
Gap assessment, policies, controls and evidence up to certification.
DPDP Act & GDPR privacy
Data mapping, consent, notices and breach processes for privacy law.
CERT-In & RBI / SEBI guidelines
Logging, incident reporting and cyber-security frameworks for India's regulated sectors.
PCI DSS
Scoping, segmentation testing and readiness for card payment environments.
Third-party risk
Security reviews of the vendors and partners who handle your data.
Virtual CISO
Senior security leadership, roadmap and board reporting, part-time.
Build securely
Secure engineering

Stop new weaknesses at the source, in your code and pipelines.

Secure code review
Manual and automated review of critical code paths.
DevSecOps
Security checks built into your CI/CD pipeline, without slowing releases.
Security architecture review
Design review of new systems, cloud landing zones and integrations.
Re-testing & verification
Confirmation that fixes work, with updated evidence for auditors.
Technology that powers this solution

Powered by mAUDIT.

mAUDIT is our own website security testing platform. An AI tester probes a site the way an attacker would, logged in with test accounts; an Infoesearch engineer checks every finding before it reaches you; and the report gives proof and the fix for each problem.

It only tests sites whose ownership has been proven and whose owner has authorised the test in writing. In enterprise engagements it gives our testers wide, fast coverage, so their time goes to the logic flaws and chained attacks that need a person.
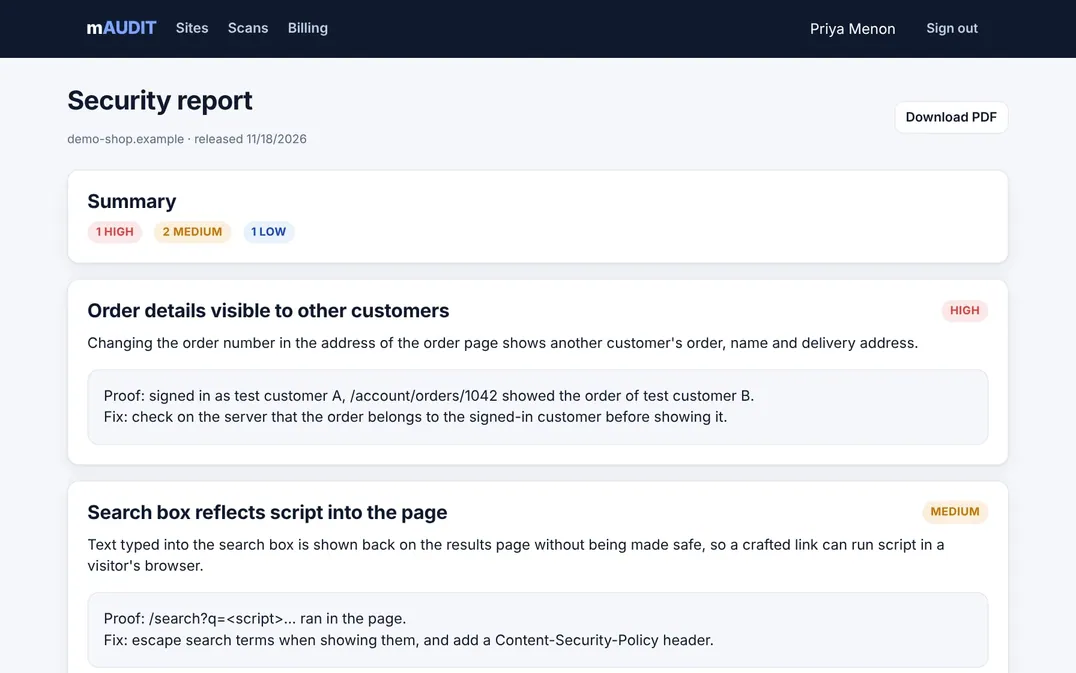
maudit.cc/scans/42/report
An mAUDIT security report with four findings ranked by severity
mAUDIT
Engineer-checked findings · proof · fixes
How we work

From scope to sign-off, five steps.

01
Scope

Agree what to protect, which standards apply, the rules of engagement and the timeline.

02
Authorise

Ownership is verified and written authorisation signed before any test begins.

03
Assess

AI covers the ground at speed; engineers go deep on logic flaws and chained attacks.

04
Verify & report

Every finding confirmed by a person, ranked by risk, with proof and a clear fix.

05
Fix & re-test

We help your team remediate, re-test to confirm, and hand over audit-ready evidence.

Standards we work to

Findings and evidence mapped to the frameworks your auditors use.

OWASP Top 10 OWASP API Security Top 10 OWASP ASVS & MASVS NIST Cybersecurity Framework MITRE ATT&CK ISO/IEC 27001 SOC 2 PCI DSS DPDP Act 2023 CERT-In Directions GDPR CIS Benchmarks
Industries we serve

Wherever data, money or reputation is at stake.

BFSI & Fintech
Payments, lending, RBI & SEBI compliance
E-commerce & Retail
Storefronts, checkout, customer data
Technology & SaaS
Products, APIs, SOC 2 for customers
Media & Entertainment
OTT platforms, content and accounts
Healthcare
Patient data and connected systems
Government & Public Sector
Citizen services and critical data
Why Infoesearch

Fewer alarms, more answers, and someone accountable for each one.

Human in Command, by default

AI widens and speeds up coverage; engineers confirm every finding and own every recommendation.

Proof, not possibilities

Each finding comes with evidence of how it was found and the change that closes it, so your developers can act at once.

Authorised and on the record

Ownership checks and written authorisation before any test, with a record of who approved what, and when.

One partner, joined-up work

Test results feed monitoring and compliance evidence, instead of sitting in separate vendors' reports.

Frequently asked questions

Questions we hear most.

Know where you stand before someone else finds out.

Tell us what you need to protect, the standard you have to meet and your deadline. We'll scope the right mix of testing, monitoring and compliance work, and start with what matters most.

INFOeSearch, Complexity to Clarity
Powered by GLIP
Hyderabad · Dallas · Omaha
Newsletter
Intelligence, in your inbox.

Monthly notes on localization, media intelligence and trust & safety. No noise, just the signal.

© 2026 Infoesearch Information Technology Enabled Services Pvt. Ltd. · All rights reserved
Cyber Security · A solution area of Infoesearch

Find the weak spots, fix what is real, and prove you are secure.

Enterprise security testing, monitoring, response and compliance, run the Infoesearch way: AI does the heavy, repetitive work, and security engineers confirm every finding and own every recommendation. No alert floods, no unverified reports.

At a glance
{{ g.label }} {{ g.value }}
The challenge

Attackers only need one gap. Most security teams cannot look everywhere at once.

{{ c.title }}

{{ c.body }}

Our solution

One security partner, from the first test to the audit report.

Infoesearch brings testing, monitoring, response and compliance under one roof, so the weaknesses found in a test feed straight into the fixes, the monitoring rules and the evidence your auditors ask for, instead of living in four vendors' reports.

It is the same Human in Command model we run across our media, localization and trust & safety work: AI covers the ground quickly and tirelessly, and experienced people decide what is real, what matters most and what to do about it.

Enterprise services

Every security discipline an enterprise needs, under one roof.

Take one service or the whole programme: as a one-off project, a yearly retainer, or a fully managed service. Every engagement is scoped with you, and nothing is tested without written authorisation.

{{ g.tag }}
{{ g.title }}

{{ g.intro }}

{{ s.name }} mAUDIT
{{ s.desc }}
Technology that powers this solution

Powered by mAUDIT.

mAUDIT is our own website security testing platform. An AI tester probes a site the way an attacker would, logged in with test accounts; an Infoesearch engineer checks every finding before it reaches you; and the report gives proof and the fix for each problem.

It only tests sites whose ownership has been proven and whose owner has authorised the test in writing. In enterprise engagements it gives our testers wide, fast coverage, so their time goes to the logic flaws and chained attacks that need a person.

maudit.cc/scans/42/report
An mAUDIT security report with four findings ranked by severity
mAUDIT
Engineer-checked findings · proof · fixes
How we work

From scope to sign-off, five steps.

{{ s.no }}
{{ s.title }}

{{ s.body }}

Standards we work to

Findings and evidence mapped to the frameworks your auditors use.

{{ s }}
Industries we serve

Wherever data, money or reputation is at stake.

{{ i.name }}
{{ i.note }}
Why Infoesearch

Fewer alarms, more answers, and someone accountable for each one.

{{ w.title }}

{{ w.body }}

Frequently asked questions

Questions we hear most.

{{ f.a }}

Know where you stand before someone else finds out.

Tell us what you need to protect, the standard you have to meet and your deadline. We'll scope the right mix of testing, monitoring and compliance work, and start with what matters most.